Governance, risk and compliance, run for you
Greg Shine · CISSP · PMP · EU DPO
A standing security and governance function for small and medium-sized enterprises. One office runs the obligations, controls and evidence, and senior CISO or DPO leadership attaches only where the business needs it.
- DORA
- NIS2
- EU AI Act
- ISO/IEC 27001
- NIST SP 800-53
- GDPR
The core engagement
One office at the centre.
A standing function rather than a project with an end date. The operating rhythm, ownership and evidence keep controls working between audits, assessments and board cycles.
- ■Obligation mapping across DORA, NIS2, EU AI Act and GDPR
- ■Control ownership, cadence and evidence
- ■Third-party risk and continuous monitoring
- ■Audit preparation and customer assurance
+
Attach when security leadership is the gap
Fractional CISO
Set direction, make risk decisions and translate technical reality for the board, without the delay of a full-time executive hire.
- Security strategy and roadmap
- Incident readiness and reporting
- Certification and assurance leadership
+
Attach when data protection needs an owner
Fractional DPO
Independent, proportionate data protection that turns GDPR obligations into working practice and clear evidence.
- DPIAs, records and policy
- DSAR and breach oversight
- Regulator readiness
The business case
AFractional leadership is not the same job at a discount. It is a deliberate choice to secure experienced direction at the level and pace the business needs now.
Buy the leadership you need
Senior judgement scaled to the work in front of you, without a permanent executive role before demand justifies it.
Move while the risk is live
Recruitment and notice periods leave risks unowned. Fractional support starts sooner.
Reduce the hiring commitment
The case is broader than salary: recruitment, benefits, management time and vacancy risk.
From risk to evidence
B01
Assess
Business context, obligations, current controls and material risks.
02
Prioritise
A risk-led roadmap, urgent decisions and foundations first.
03
Operationalise
Owners, routines and governance in day-to-day delivery.
04
Evidence
Visible progress and records auditors and regulators expect.
The partner platform.
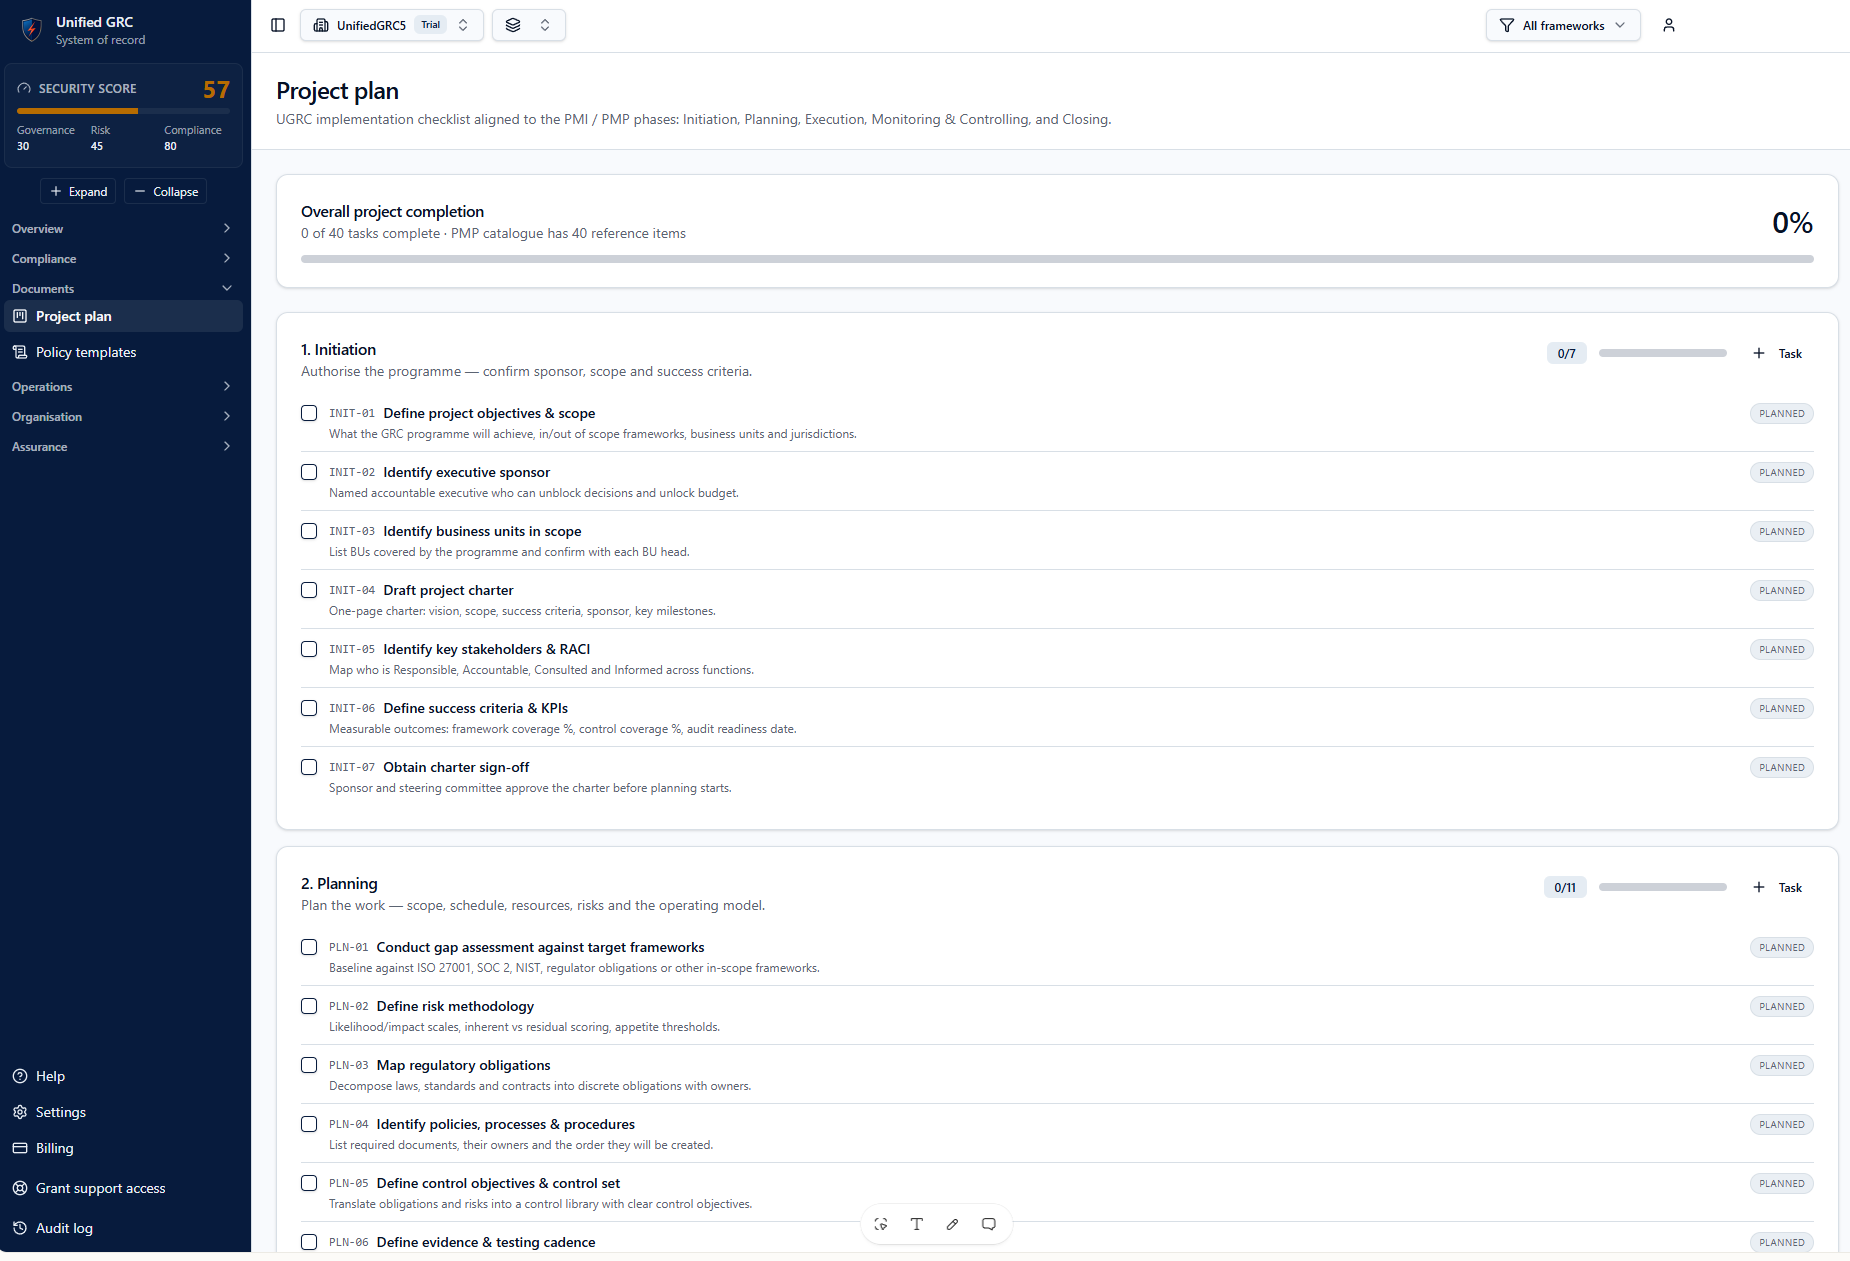
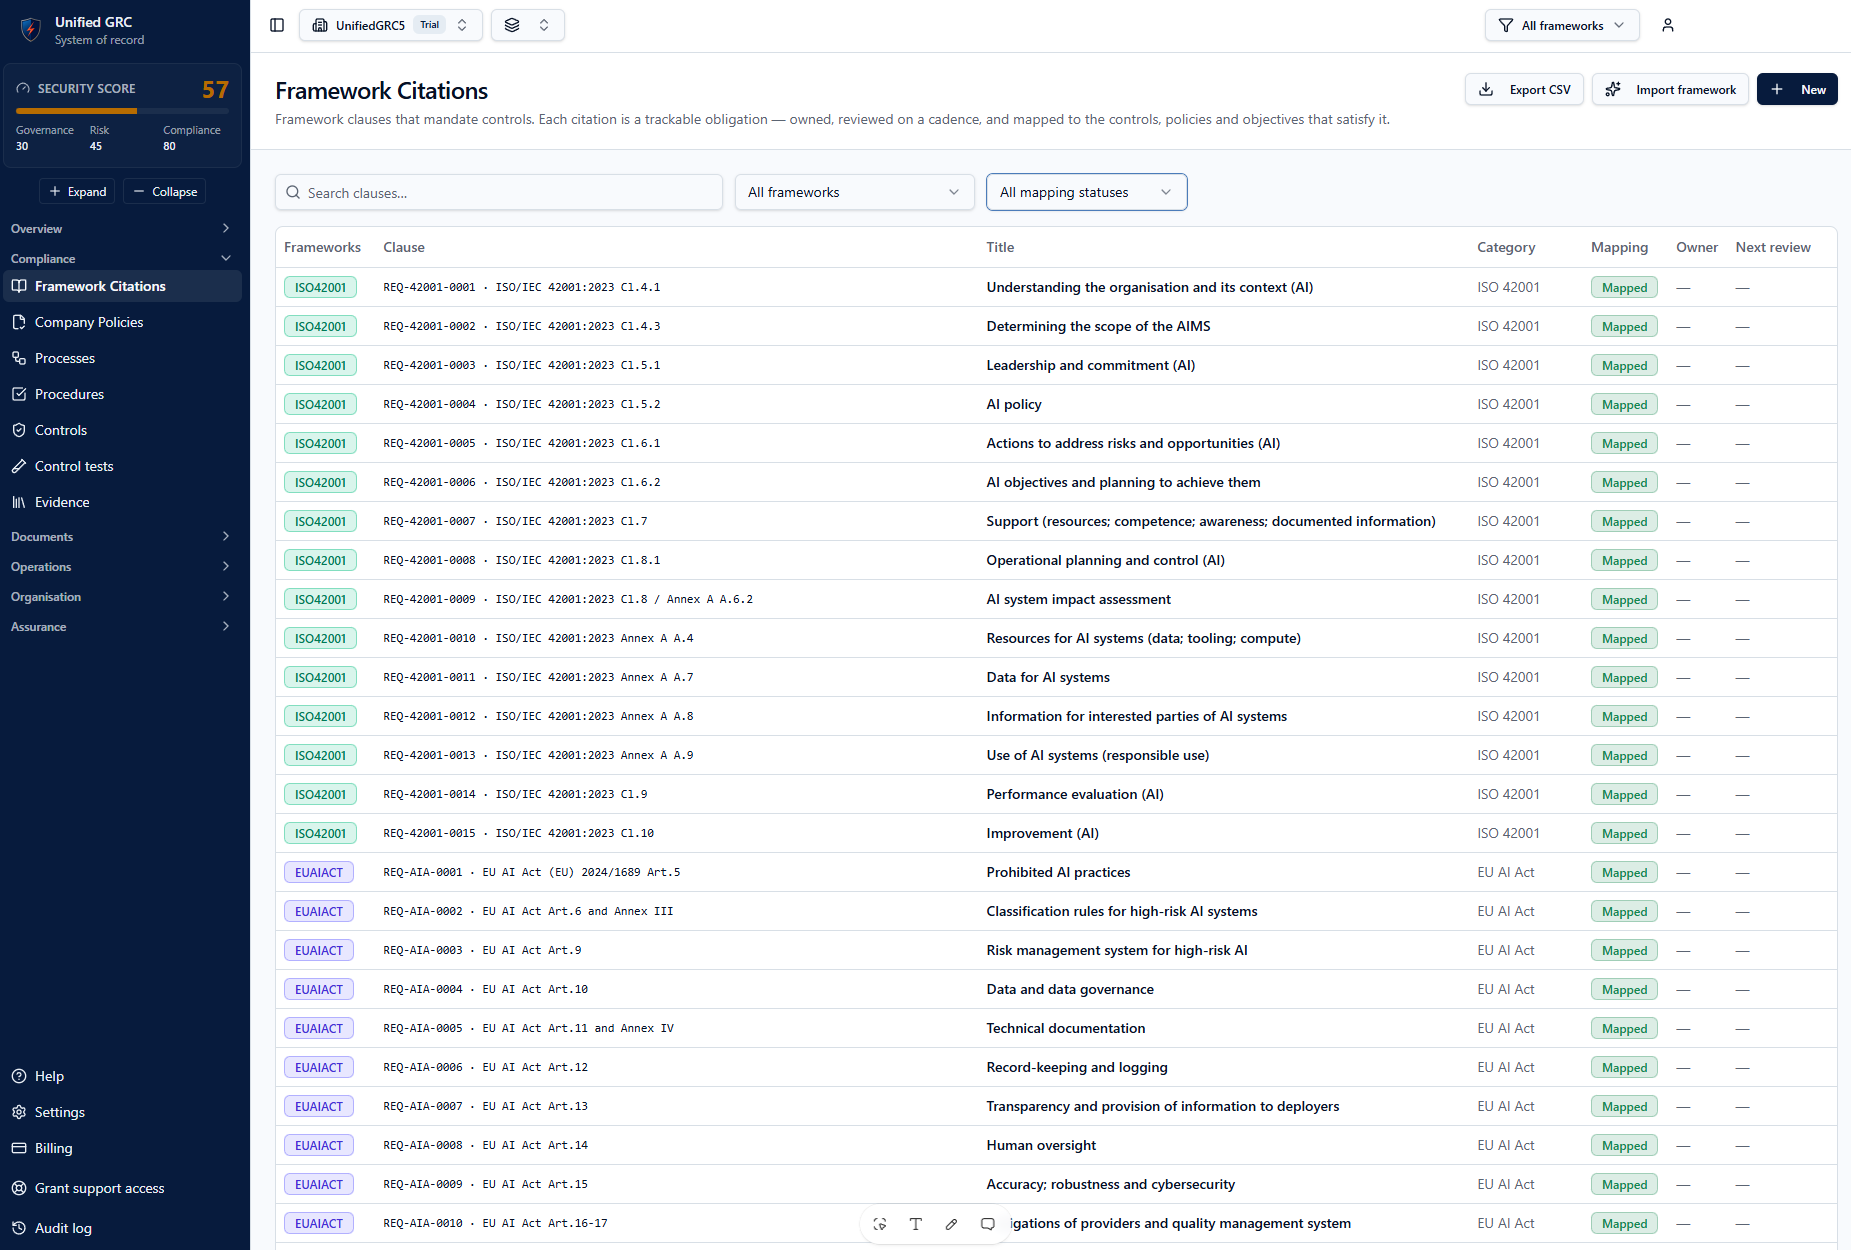
Developed in partnership with Greg Shine, Forusna keeps mapped frameworks, policies, controls, suppliers, plans and evidence in one working system.
Visit forusna.com →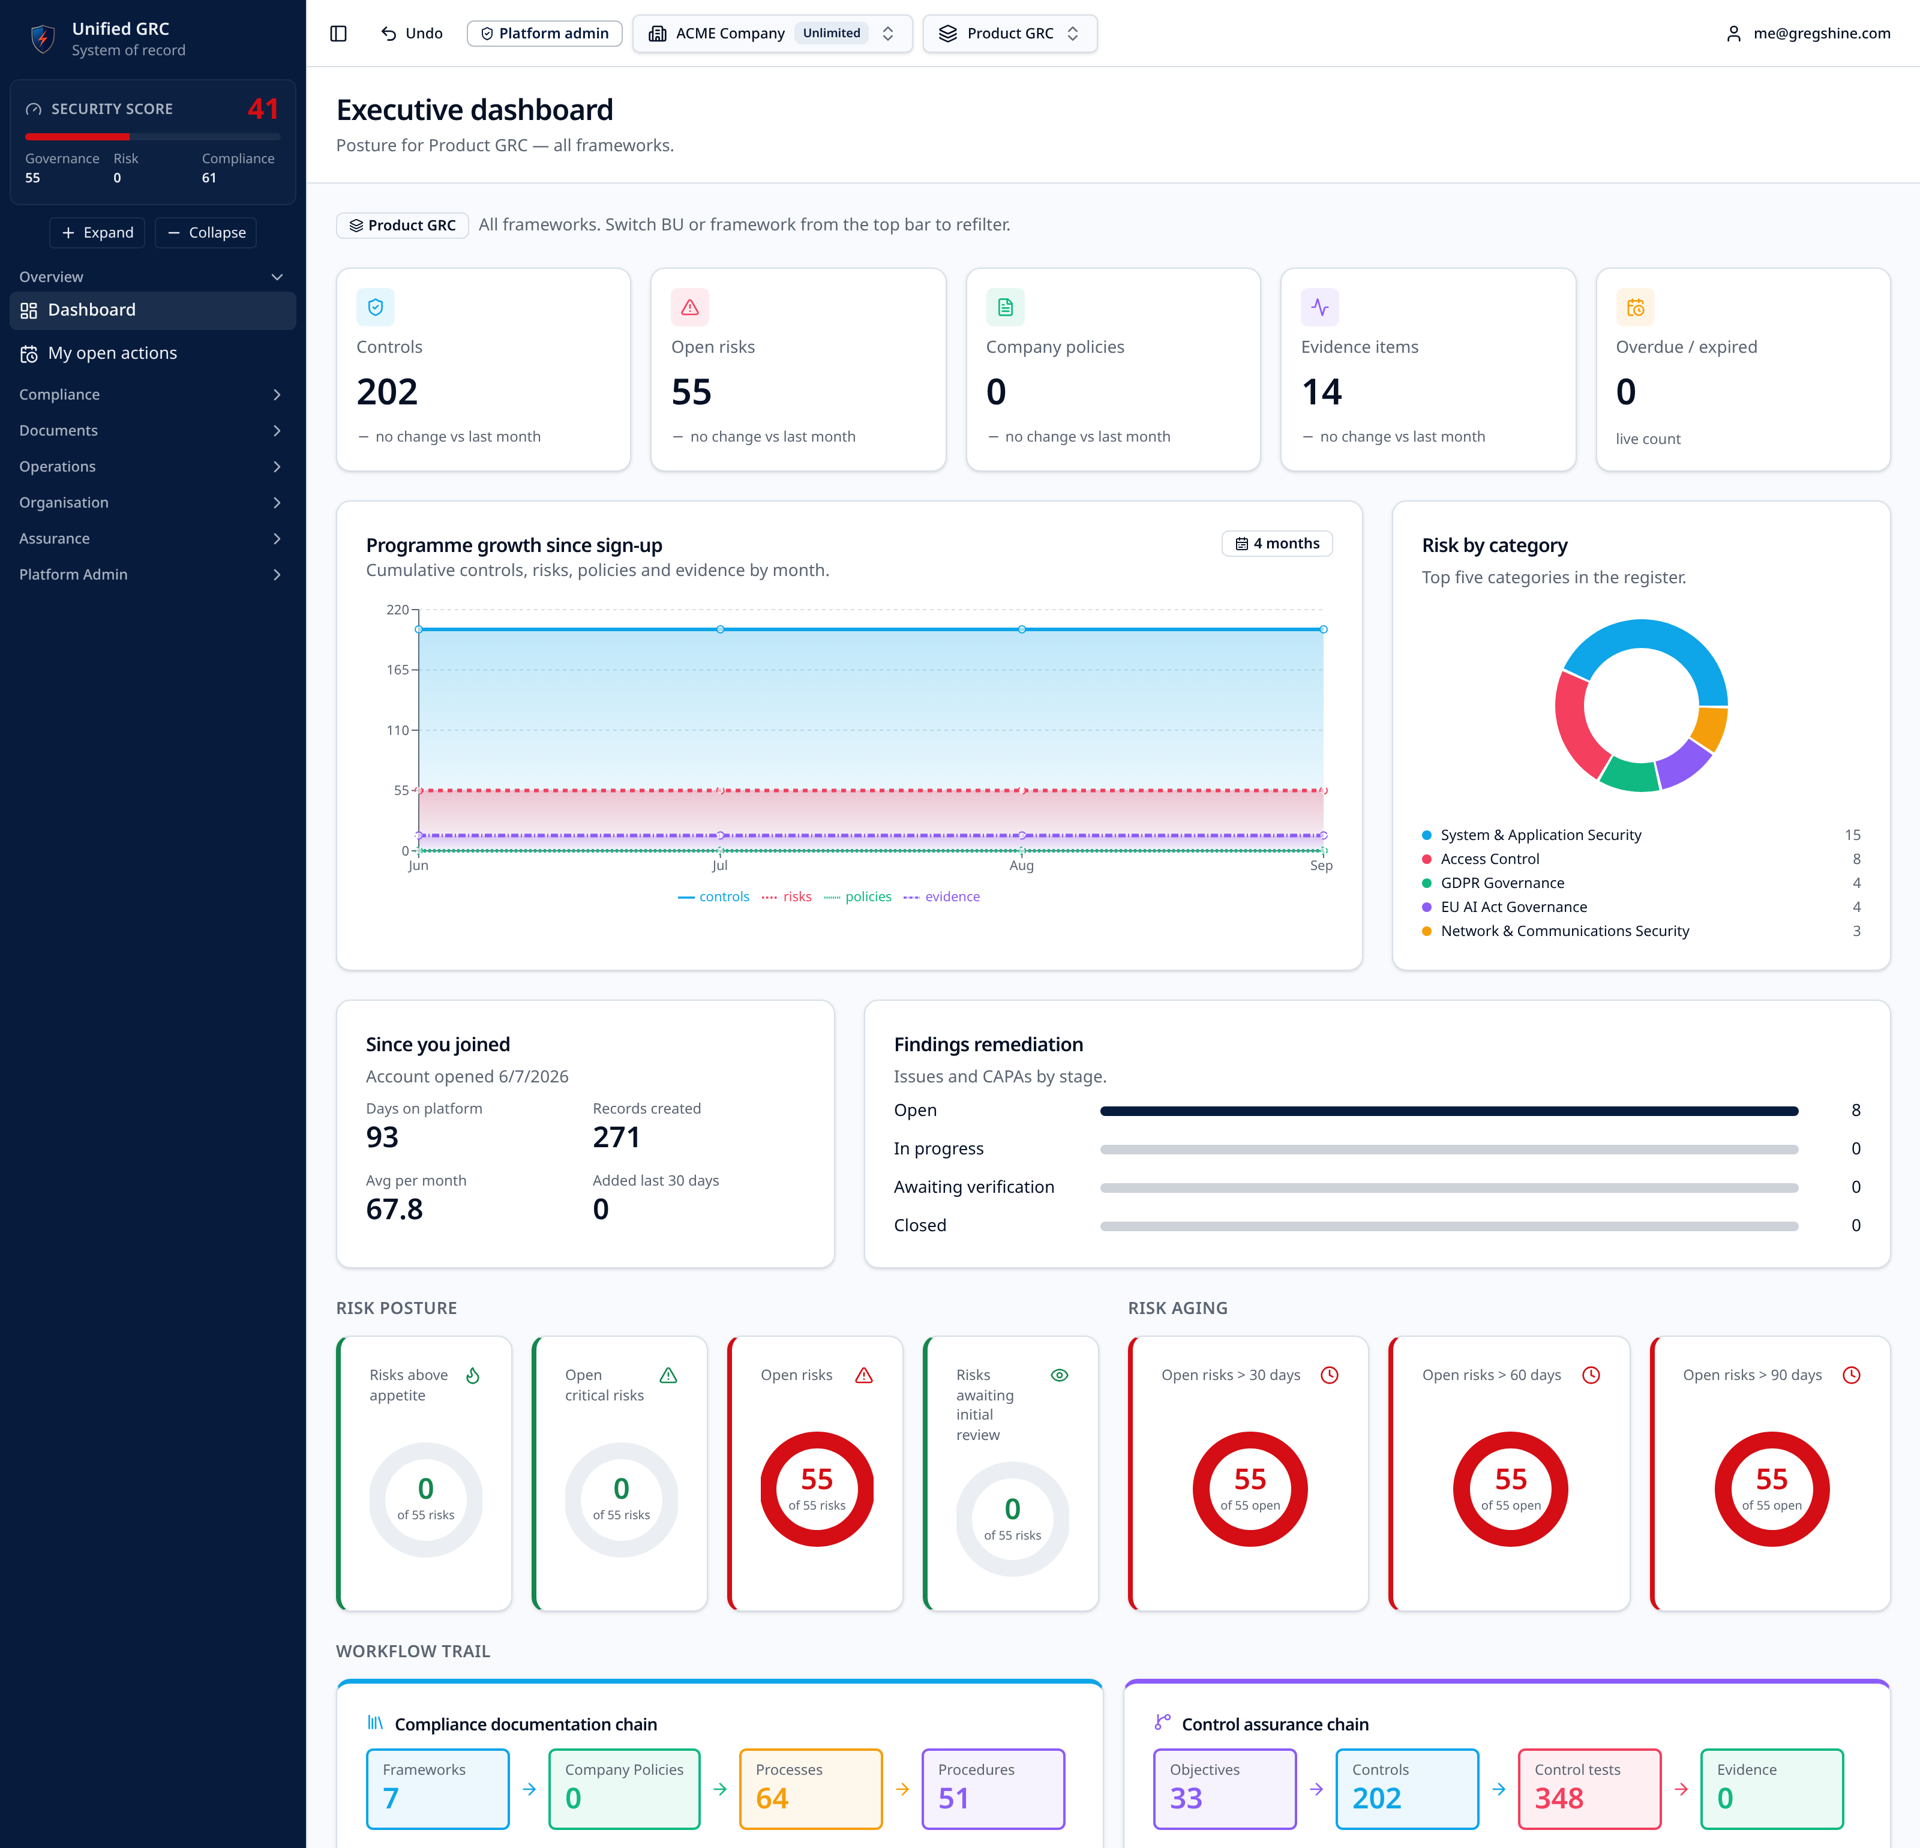
60 seconds
CAn honest fit test
Works best when a business needs experienced security or GRC leadership, but not that executive capacity every working day: regulatory change, certification, customer assurance or rapid growth.
When to hire instead
When the workload becomes consistently full-time, a permanent hire may be the better choice. A fractional engagement can define the mandate and priorities before recruitment begins.